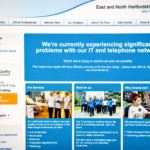
England’s healthcare system came under a withering cyberattack Friday morning, with ” at least 25 ” hospitals across the country falling prey to ransomware that locked doctors and employees out of critical systems and networks. The UK government now reports that this is not a (relatively) isolated attack but rather a single front in a massive regionwide digital assault. #nhscyberattack pic.twitter.com/SovgQejl3X — gigi.h (@fendifille) May 12, 2017 The attack has impacted hospitals and transportation infrastructure across Europe, Russia and Asia. Organizations in dozens of countries have all been hit with the same ransomware program, a variant of the WannaCry virus, spouting the same ransom note and demanding $300 for the encryption key, with the demand escalating as time passes. The virus’s infection vector appears to through a known vulnerability, originally exploited and developed by the National Security Agency. That information was subsequently leaked by the hacking group known as Shadow Broker which has been dumping its cache of purloined NSA hacking tools onto the internet since last year. The virus appears to have originally spread via email as compressed file attachment so, like last week’s Google Docs issue, make sure you confirm that you email’s attachments are legit before clicking on them. Also, make sure your computers are using software that’s still receiving security updates, and that you’ve installed the latest updates available. Microsoft released a fix for the exploit used as a part of its March “Patch Tuesday” release, but unpatched Windows systems remain vulnerable. Update : Reuters reports a statement from Microsoft indicating that engineers have added detection and protection against the “Ransom:Win32.WannaCrypt” malware, so make sure your Windows Defender or other antivirus is updated before logging on to any corporate networks that may be infected. In a statement, a FedEx representative confirmed its systems are being impacted, saying “Like many other companies, FedEx is experiencing interference with some of our Windows-based systems caused by malware. We are implementing remediation steps as quickly as possible. We regret any inconvenience to our customers.” Source: New York Times
More:
‘WannaCry’ ransomware attack spreads worldwide (update)
 Bikers interested in going green have reason to rejoice today. Harley-Davidson has already shown off its prototype Livewire electric bike, and it’s promised to offer you a real one in the next five years . Today, the motorcycle manufacturer said it has plans to make 100 new motorcycles over the next 10 years, including an entire range of electric vehicles. Vice president Bill Davidson confirmed that electric bikes are Harley-Davidson’s future to Drive magazine while in Sydney to celebrate the brand’s 100th anniversary in Australia. While an electric Harley won’t have the signature engine boom that its combustion-powered bikes have, Davidson said that the company is working on a sound that he likens to a jet engine. “It is an amazing motorcycle, ” he told Drive . “While it doesn’t have a 45-degree, pushrod twin-cylinder engine it has the performance expected from a Harley Davidson even if it won’t sound the same, ” he said. So far, we’ve only seen the one Livewire concept model with a limited top speed and range, it’s likely thHarleyely-Davidson will create both sport and cruiser-style bikes to appeal to both the speed freaks and the touring bikers. Davidson noted that as automated cars become more ubiquitous, driving enthusiasts may turn to motorcycles to get their manual fix, telling Drive , “I think the more automatic cars [happen], motorcycling will become more appealing. I see it as a huge opportunity.” Via: Autoblog Source: Drive
 President Trump on Thursday signed a long-delayed executive order on cybersecurity that “makes clear that agency heads will be held accountable for protecting their networks, and calls on government and industry to reduce the threat from automated attacks on the internet, ” reports The Washington Post. From the report: Picking up on themes advanced by the Obama administration, Trump’s order also requires agency heads to use Commerce Department guidelines to manage risk to their systems. It commissions reports to assess the country’s ability to withstand an attack on the electric grid and to spell out the strategic options for deterring adversaries in cyberspace. [Thomas Bossert, Trump’s homeland security adviser] said the order was not, however, prompted by Russia’s targeting of electoral systems last year. In fact, the order is silent on addressing the security of electoral systems or cyber-enabled operations to influence elections, which became a significant area of concern during last year’s presidential campaign. The Department of Homeland Security in January declared election systems “critical infrastructure.” The executive order also does not address offensive cyber operations, which are generally classified. This is an area in which the Trump administration is expected to be more forward-leaning than its predecessor. Nor does it spell out what type of cyberattack would constitute an “act of war” or what response the attack would invite. “We’re not going to draw a red line, ” Bossert said, adding that the White House does not “want to telegraph our punches.” The order places the defense secretary and the head of the intelligence community in charge of protecting “national security” systems that operate classified and military networks. But the secretary of homeland security will continue to be at the center of the national plan for protecting critical infrastructure, such as the electric grid and financial sector. Read more of this story at Slashdot.